Managed Endpoint Security: Complete Guide to EDR, Antivirus, and XDR Cyber Security
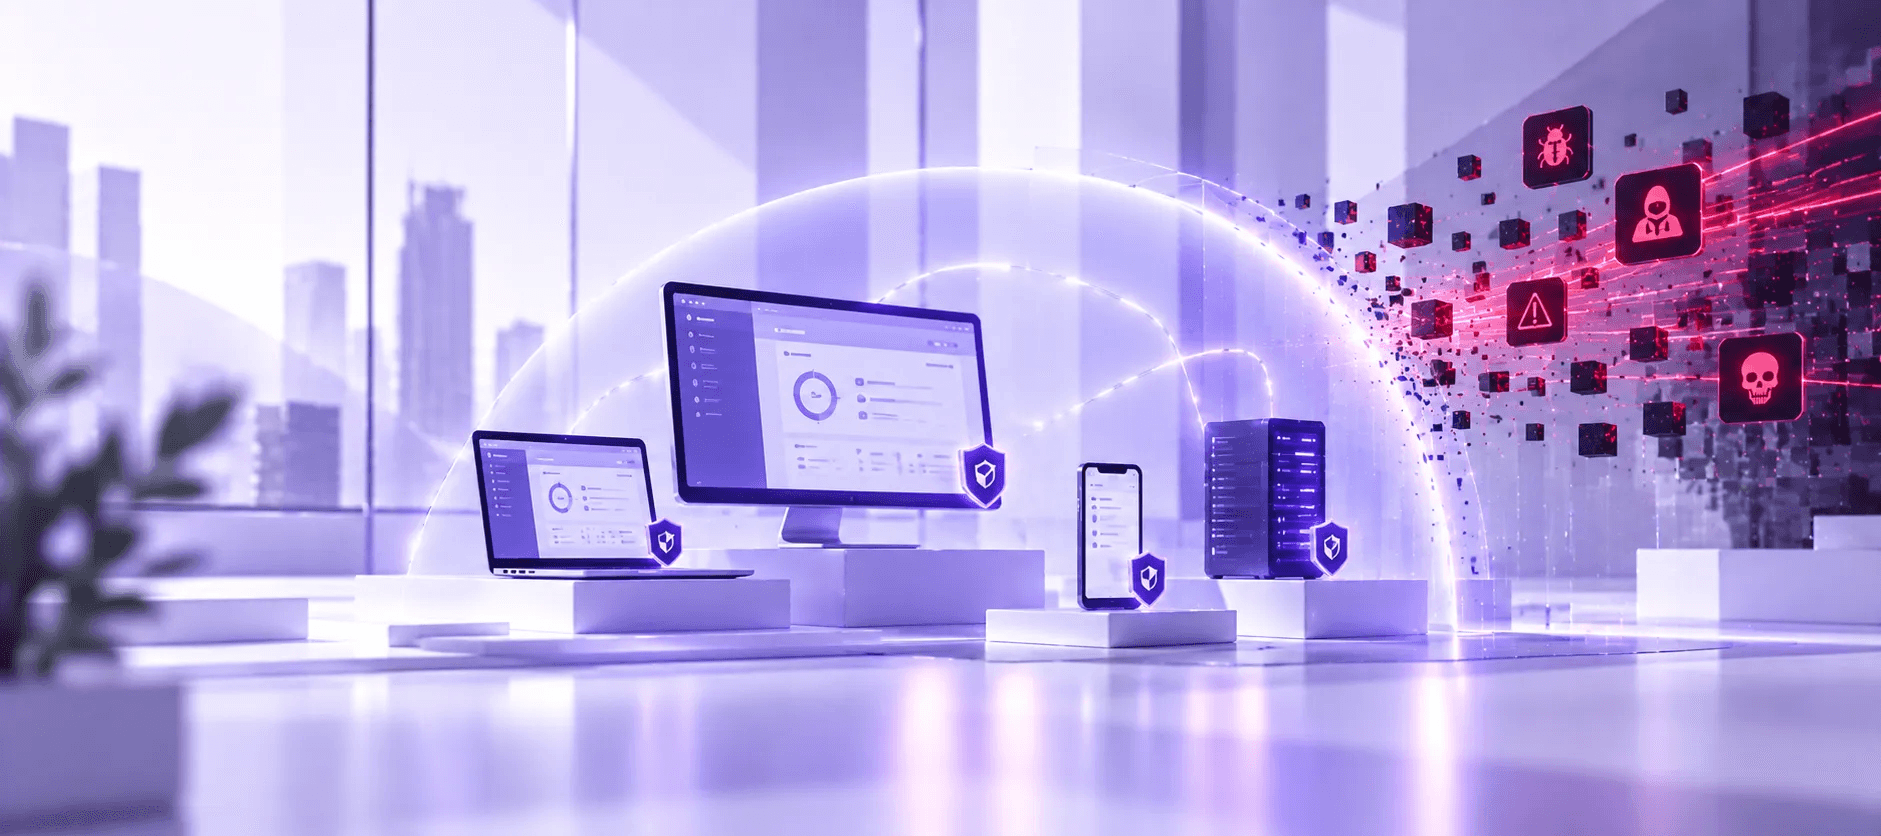
Modern digital workplaces face constant cyber threats targeting laptops, servers, and mobile devices. Traditional perimeter defenses no longer protect distributed teams working across global networks. Because of this shift, organizations increasingly rely on managed endpoint security to monitor and protect vulnerable access points. Let's unpack how combining human expertise with advanced threat detection technology secures your entire digital ecosystem.
As cyberattacks grow more sophisticated, internal IT teams often struggle to review alerts around the clock. Managed security services bridge this gap by delivering continuous monitoring, rapid incident response, and proactive threat hunting. In this comprehensive guide, we will explore core protection layers, examine modern EDR tools, compare antivirus solutions, and look at advanced XDR cyber security platforms.
Key Takeaways:
- Managed endpoint security combines third-party expertise with 24/7 monitoring tools.
- Endpoint Detection and Response (EDR) provides deep visibility into active device threats.
- Extended Detection and Response (XDR) unifies telemetry across endpoints, email, and cloud workloads.
- Structured planning, proper governance, and continuous validation ensure long-term cyber resilience.
What is Managed Endpoint Security?
Managed endpoint security is a specialized service that monitors, detects, and neutralizes cyber threats across an organization's devices. Instead of relying solely on internal staff, companies partner with external security providers to oversee corporate laptops, mobile phones, and cloud servers. This proactive approach ensures threats are addressed before they cause operational disruption.
In a Zero Trust architecture, devices serve as a primary trust evaluation point. Even when a user's identity is verified, access decisions depend heavily on the security health and risk state of the device. Managed endpoint services continuously assess device posture to prevent compromised hardware from entering the corporate network.
Industry Insight: Recent cybersecurity studies indicate that organizations utilizing managed security services detect and contain threats up to 50 percent faster than those relying solely on internal teams.
Foundational Assessment and Baseline Metrics
Before deploying a managed security solution, your organization must conduct a thorough foundational assessment. Map out all active device workflows, identify potential bottlenecks, and run pain-point surveys across your IT departments. Baseline metrics help prioritize investments and target tangible risk reduction from day one.
Organizations often discover unmanaged or shadow IT devices during this audit phase. Documenting every access point closes security gaps and ensures consistent software patch levels across the enterprise. For complex infrastructure transformations, partnering with experts can streamline your development and security integration workflows.
What is EDR?
Endpoint Detection and Response (EDR) refers to software tools that continuously monitor end-user devices to detect and investigate suspicious activities. Unlike legacy security tools that rely on static signatures, EDR captures behavioral telemetry in real-time. Security analysts use this data to hunt for stealthy threats that bypass traditional preventive controls.
When an anomaly occurs, EDR systems automatically trigger alerts and record detailed attack timelines. Analysts can isolate infected devices from the network instantly, preventing lateral movement. This capability transforms reactive defense into proactive threat mitigation.
Action Checklist for EDR Deployment:
- Inventory all enterprise endpoints requiring continuous behavioral monitoring.
- Deploy lightweight agents across Windows, macOS, and Linux environments.
- Establish automated containment rules for high-severity behavioral alerts.
- Train security teams on root-cause analysis and threat-hunting workflows.
Use Case Prioritization for Threat Defense
Deploying advanced security tools requires clear use case prioritization based on business impact and technical feasibility. Score potential deployment targets by calculating risk reduction and implementation complexity. High-impact and high-feasibility endpoints, such as executive laptops and financial databases, should form your first-wave pilot group.
Measuring pilot success relies on tracking metrics like mean time to detect (MTTD) and mean time to respond (MTTR). Once initial pilots prove stable, expand coverage to remote worker devices and auxiliary servers. This phased rollout minimizes operational friction while maximizing security ROI.
EDR vs Antivirus: Key Differences
Traditional antivirus (AV) software scans files against a database of known malware signatures to block known threats. In contrast, EDR focuses on behavioral analysis, monitoring ongoing system activity to catch zero-day exploits and fileless attacks. Understanding the differences between EDR and antivirus helps organizations build a balanced defense strategy.
Antivirus acts as a digital bouncer, checking IDs at the door against a blacklist of known bad actors. EDR acts as an internal security guard, patrolling the building and watching for suspicious behavior even if the intruder entered with a valid pass. Modern organizations often combine both technologies for comprehensive protection.
Survey Says: Industry data shows that over 75 percent of successful data breaches involve sophisticated techniques that legacy antivirus alone cannot detect or prevent.
Comparing Capabilities and Operational Scope
Traditional antivirus solutions operate reactively, requiring regular signature updates to identify new malware strains. When a new threat emerges before a signature update exists, antivirus tools often fail to spot the intrusion. EDR mitigates this risk by analyzing process execution, registry modifications, and network connections.
Furthermore, EDR provides deep forensic data that helps security teams understand how an attack unfolded. Antivirus simply quarantines a file and alerts the administrator without offering broader context. Upgrading from legacy AV to EDR is a vital step for maturing your corporate security posture.
Traditional Antivirus vs. EDR: Core Capabilities
| Security Dimension | Traditional Antivirus | Endpoint Detection & Response (EDR) |
|---|---|---|
| Primary Detection Method | Relies on static databases of known malware signatures. | Monitors real-time behavioral telemetry and system activity. |
| Threat Scope | Blocks recognized files and known blacklisted actors. | Hunts for stealthy threats, zero-day exploits, and fileless attacks. |
| Incident Response | Typically removes or quarantines infected files upon scanning. | Records attack timelines and allows instant isolation of infected devices. |
XDR Cyber Security: The Next Evolution
Extended Detection and Response (XDR) takes endpoint security to the next level by unifying telemetry across multiple security layers. XDR cyber security platforms integrate data from endpoints, cloud workloads, email gateways, and network traffic into a single console. This holistic visibility allows security systems to correlate signals that might look harmless in isolation.
For example, an unusual login attempt on a cloud application combined with a strange script execution on an endpoint could trigger an XDR alert. Traditional EDR tools might miss the cross-channel correlation. XDR connects the dots across your entire infrastructure to stop complex multi-stage attacks.
Key Takeaways on XDR:
- XDR unifies data from endpoints, cloud environments, and email systems.
- Cross-layer correlation detects advanced multi-vector cyberattacks faster.
- Automated response workflows reduce analyst burnout and alert fatigue.
Governance, Validation, and Operational Controls
Implementing advanced detection platforms requires strict operational governance beyond technical security configurations. Document a formal governance framework that defines acceptable use rules, data handling boundaries, and regulatory compliance obligations. Assign clear ownership of security policies to a dedicated IT committee or security leadership team.
Validation and fact-checking protocols remain critical when utilizing automated response tools. Establish multi-layer review processes for automated containment actions to prevent accidental service outages. Independent professional judgment ensures that automated systems do not disrupt legitimate business operations during false-positive events.
Evolution of Endpoint Threat Defense
| Defense Level | Core Focus Area | Visibility and Integration |
|---|---|---|
| Traditional AV | File scanning and basic signature matching. | Limited to standalone device file checks. |
| EDR | Real-time endpoint telemetry and behavioral anomaly detection. | Focused strictly on end-user device monitoring and isolation. |
| XDR Cyber Security | Cross-layer telemetry unification across multiple security vectors. | Integrates data from endpoints, cloud workloads, email, and network traffic. |
Structured Training and Adoption Protocols
Technology alone cannot protect an organization without proper user adoption and team training. Build a structured training protocol that covers practical tool usage, effective incident response workflows, and governance guidelines. Awareness of limitations, such as potential system alerts and phishing tactics, empowers employees to act as the first line of defense.
Deliver training through bite-sized modules, lunch-and-learn sessions, and internal security champions. Engaging busy professionals through practical, hands-on examples ensures high participation rates. For organizations scaling their digital initiatives, expert guidance in marketing and secure internal communications can support widespread adoption.
Your Managed Endpoint Security Roadmap
Navigating the transition to managed endpoint security requires a structured, phased approach. Consolidating your strategy into clear operational phases ensures comprehensive risk coverage and measurable business value.
Your Managed Endpoint Security Roadmap:
- Assess and Strategize: Map all network endpoints, conduct baseline risk audits, and establish core security metrics. Expert Tip: Involve cross-functional department heads early to capture unmanaged shadow devices.
- Pilot and Learn: Deploy EDR tools across high-impact endpoints as a first-wave test group. Expert Tip: Track mean time to detect metrics closely during the pilot phase to fine-tune alert thresholds.
- Govern and Secure: Document formal governance policies, acceptable use rules, and automated containment protocols. Expert Tip: Establish multi-layer validation reviews to prevent automated actions from disrupting business workflows.
- Measure and Refine: Connect security performance to business ROI, turnaround speed, and risk reduction. Expert Tip: Review incident reports monthly to adapt defenses against emerging threat trends.
- Scale and Evolve: Expand protection into XDR cyber security platforms that unify cloud and network telemetry. Expert Tip: Partner with experienced providers to future-proof your cybersecurity infrastructure.
Conclusion
Securing modern enterprise assets requires moving beyond legacy antivirus tools into sophisticated managed endpoint security frameworks. By understanding what EDR offers, comparing EDR vs antivirus capabilities, and adopting advanced XDR cyber security platforms, organizations can neutralize complex threats effectively.
Implementing a structured roadmap—from initial assessment and use-case prioritization to rigorous governance and continuous training—ensures long-term cyber resilience. Take proactive steps today to safeguard your digital ecosystem and protect your valuable business assets against evolving cyber threats.